AI software
AI-Jailor: capability scoping against indirect prompt injection
Clement Nana Aidoo
77%
Share of 949 user × injection pairs on AgentDojo v1.2 where the manifest denies a tool the attack needs (95% interval 70–82%)
Summary
Defences against indirect prompt injection that work well today put a language model in the loop, which adds model calls and latency to every task. We ask how much protection a tool-calling agent can get for free, from a tool whitelist built once from the user’s instruction.
Our summary. The archived abstract is the authority: doi:10.5281/zenodo.23636157.
Archived title: How Much Prompt-Injection Defense Does a Free Tool Whitelist Buy? Zero-Inference Capability Manifests for Tool-Calling Agents
What it found
- F1
capscope builds the manifest by matching stemmed action verbs against per-tool profiles written from documentation. It takes under a millisecond and makes no model call.
- F2
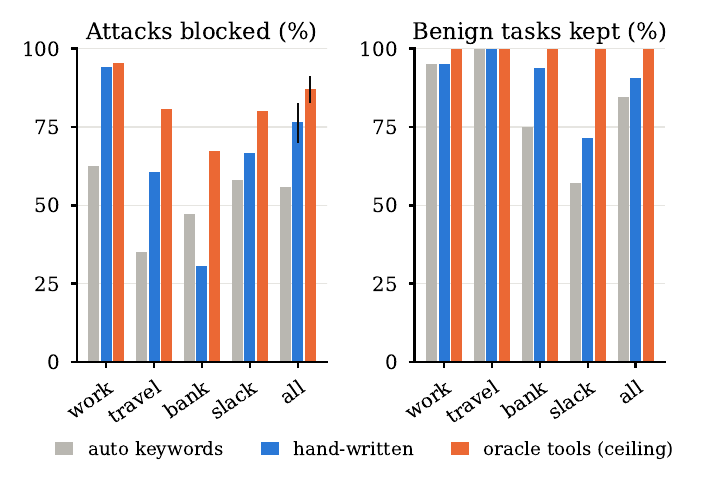
The hand-written manifest keeps every needed tool for 91% of benign tasks. Mechanically extracted keywords do much worse, blocking only 56% of pairs.
- F3
Even an oracle whitelist that knows exactly which tools each user task needs blocks only 87% of pairs. The other 13% (33% in banking) use only tools the user’s own task needs, so no tool-level policy can stop them.
Limitations
- An end-to-end evaluation with a model remains to be done.
- The evaluation is an oracle check against the benchmark’s ground-truth tool calls, not a live agent.
- The paper is still in progress. Protocol, profiles, code and per-pair results are public.
Cite
@misc{aidoo2026capscope,
  title  = {How Much Prompt-Injection Defense Does a Free Tool Whitelist Buy? Zero-Inference Capability Manifests for Tool-Calling Agents},
  author = {Aidoo, Clement Nana},
  year   = {2026},
  note   = {Paper in progress; code public},
  doi    = {10.5281/zenodo.23636157},
  url    = {https://doi.org/10.5281/zenodo.23636157}
}Evidence chain
01 · Claim
77%
02 · Figure
03 · Code
04 · Archive
Code and data